Hiding or renaming a private file on Linux doesn’t keep other people out of it, so you need to encrypt it. GPG encrypts a file with a passphrase you choose and writes the result as a separate encrypted copy.
The steps cover encrypting and decrypting a file this way, then doing the same for a whole folder with tar.
What is GPG symmetric encryption?
GPG symmetric encryption uses a passphrase to encrypt a file. GPG writes a separate encrypted file, so the readable source remains on disk.
GnuPG’s command reference documents the symmetric and decrypt operations.
A directory needs to become an archive before ordinary GPG file encryption can process it. GNU tar packages the directory tree into one file, which GPG can then encrypt.
GnuPG’s gpgtar manual also documents a directory-aware alternative.
| Task | Method | What stays on disk |
|---|---|---|
| Protect one file | GPG symmetric encryption | The source and a separate .gpg file |
| Protect a directory | tar archive followed by GPG | The source tree and encrypted archive |
| Send a file to someone | GPG public-key encryption | The recipient’s public key encrypts it, their private key decrypts it |
Hiding a file’s name is not encryption, so choose GPG when you want a private local copy.
What you need before encrypting
Have GnuPG and GNU tar installed. Prepare a source file and a directory to protect, then choose a passphrase you can retrieve later.
If you need a spare input file, use the Linux file-creation examples.
gpg --version
tar --version
mkdir -p project-files/subdir
printf 'Report content for encryption.\n' > report.txt
printf 'Project note.\n' > project-files/notes.txt
printf 'Nested note.\n' > project-files/subdir/nested.txt
- GPG encrypts a file using your passphrase, so store that passphrase somewhere you can recover it.
- Keep the plaintext source until you have decrypted and checked the encrypted copy.
- The example creates a file and a directory tree so you can follow both paths without using private data.
Encrypt and decrypt a file with GPG
Symmetric encryption fits a file that you want to protect with a passphrase you control. The encrypted output gets its own name, leaving the readable source untouched.
1. Encrypt a file with a passphrase
Run GPG’s symmetric option with an explicit output path, and it prompts for a passphrase before writing report.txt.gpg.
gpg --symmetric --output report.txt.gpg report.txt
GPG leaves the original report.txt readable beside report.txt.gpg. Keep both files until you have decrypted and compared the copy.

The encrypted output is binary, so cat displays unreadable bytes without showing whether GPG can restore it.

2. Decrypt to a named output file
Use –decrypt with –output to choose the destination. Without –output, GPG writes decrypted content to standard output.
gpg --output report-restored.txt --decrypt report.txt.gpg
GPG uses the same passphrase, though its agent may reuse a cached value, and –output writes report-restored.txt.

Archive and encrypt a directory with tar and GPG
Tar packages a directory tree into one archive file, then GPG encrypts that file. The unencrypted tar archive remains readable until GPG writes its encrypted copy.
The tar command reference explains archive creation and extraction.
1. Create an archive from the directory
Create an archive that contains the project-files directory and its nested files.
tar --create --file project-files.tar project-files/
Before GPG runs, project-files.tar remains plaintext. Anyone with access to the archive can read its contents.
2. Encrypt the tar archive
Pass the archive to GPG with the same symmetric mode used for a single file. GPG creates project-files.tar.gpg and leaves both the source directory and unencrypted tar archive in place.
gpg --symmetric --output project-files.tar.gpg project-files.tar
| Artifact | Contents | Encrypted |
|---|---|---|
| project-files/ | Original directory tree | No |
| project-files.tar | Archived copy of the tree | No |
| project-files.tar.gpg | Encrypted tar archive | Yes |

3. Decrypt and extract into a new directory
Restore the tar file to a separate path before extracting it. The directory option tells tar where to place the files, while the archive preserves the project-files folder as the top-level entry.
gpg --output project-files-restored.tar --decrypt project-files.tar.gpg
mkdir -p restored
tar --extract --file project-files-restored.tar --directory restored
The extracted tree now sits at restored/project-files, separate from the source. Gzip compression can reduce an archive’s size, but it does not replace GPG encryption.
Check the encrypted output and restored file
A .gpg suffix is only a filename, and unreadable output from cat is not proof of encryption. Use the file command to identify the encrypted data, then compare the restored file with its source.
file report.txt.gpg project-files.tar.gpg
cmp report.txt report-restored.txt
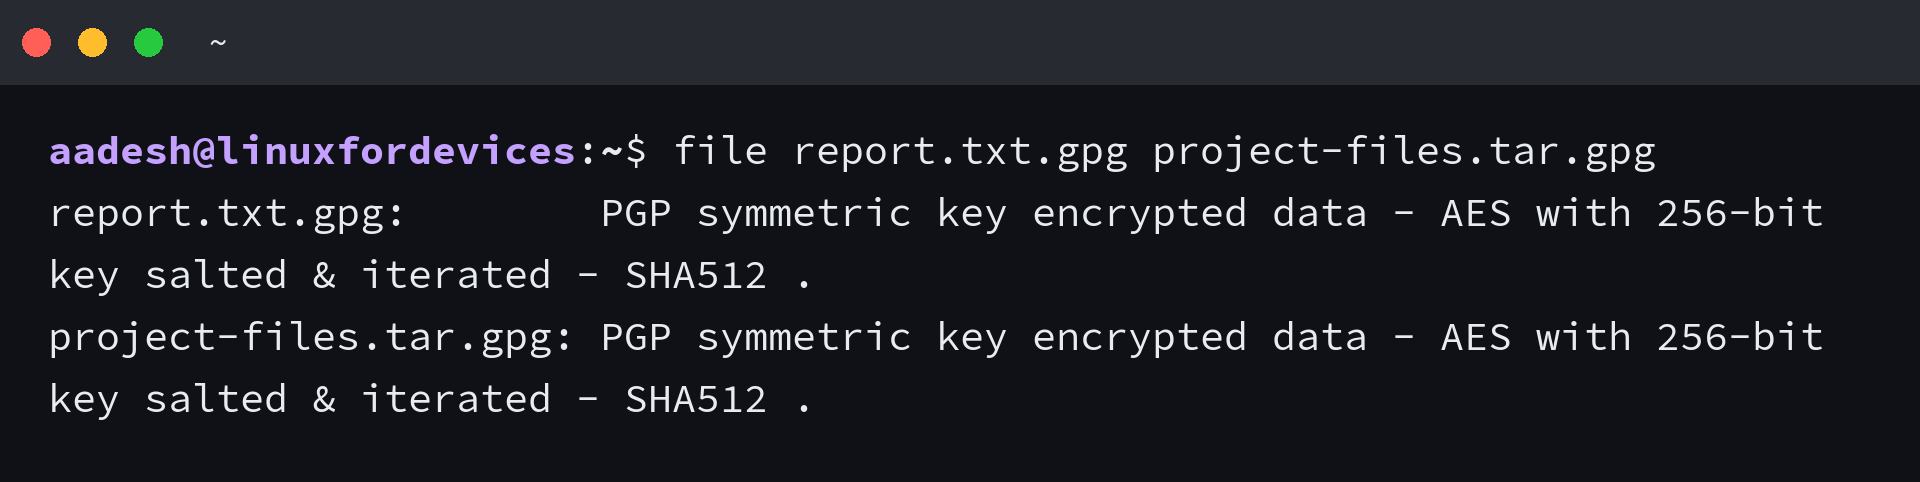
I ran file on both outputs, and it identified them as PGP symmetric-key encrypted data. cmp prints nothing when the restored file matches its source.
A nonzero exit means the files differ or a comparison failed.
- The file command identifies the kind of data in the encrypted output, but it does not prove that your passphrase can restore it.
- The cmp command returns success without printing anything when the source and restored file match byte for byte.
For another post-extraction check, use the file count command after you confirm that the restored path contains the expected tree.
Choose a passphrase or a recipient key
Symmetric encryption suits a local file when you can protect and retrieve one shared passphrase. Public-key encryption suits sending a file to someone else, because you encrypt with the recipient’s public key and they decrypt with their private key.
| Use case | GPG method | What you must keep |
|---|---|---|
| Store your own encrypted file | –symmetric | The passphrase and an intact encrypted copy |
| Send a file to another person | –encrypt with their recipient key | A verified recipient public key and your copy if you need to decrypt too |
Do not use Info-ZIP’s built-in –encrypt mode for confidential files. Info-ZIP’s encryption FAQ describes its built-in encryption as weak.
WinZip’s note on standard ZIP 2.0 encryption says the method should not be relied on for strong protection. The Linux zip and unzip commands page covers ordinary archives.

A directory is not encrypted in place by this archive workflow. If files change after you create the archive, create and encrypt a new archive so the protected copy includes those changes.
Test one restore before deleting plaintext
Keep the readable source until the encrypted copy has been decrypted and compared. Other copies may remain in backups or snapshots, so removing the source is a separate decision.
The rm command removes the file or directory entry you name, but it does not remove separate copies in backups.
diff -qr project-files/ restored/project-files/ && printf 'Directory contents match\n'
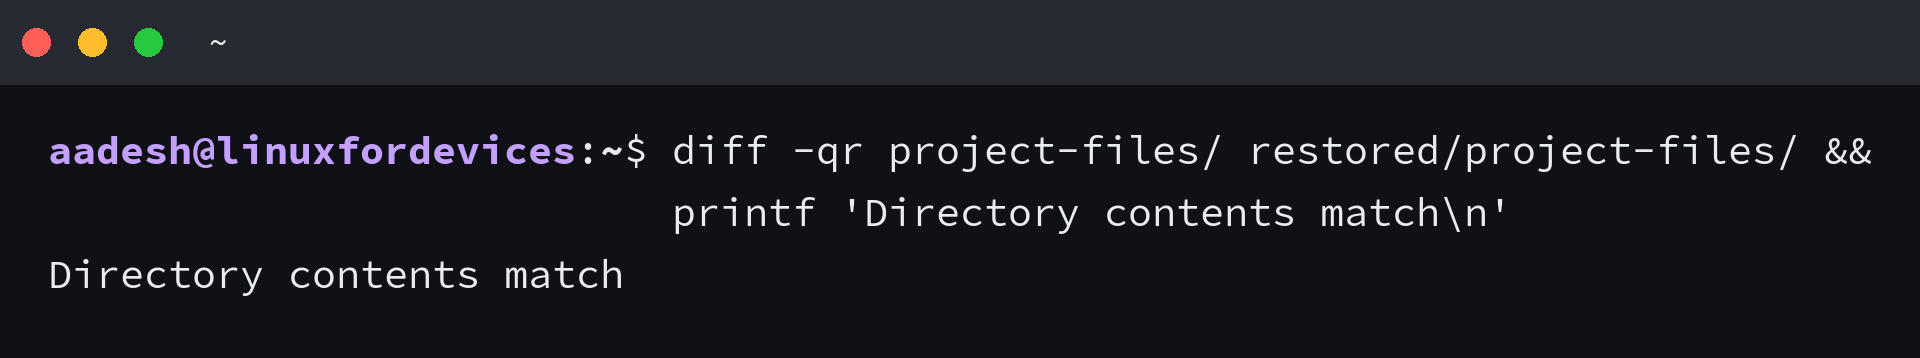
I compared the extracted project-files tree with its source, and diff found no differences. The command printed “Directory contents match” only after the comparison succeeded.
Store the passphrase separately from the encrypted archive, and keep a copy of the original until you have verified a full restore.
GPG file and directory encryption questions
GPG treats a directory archive as a file, and the passphrase remains the recovery key for its contents.
Can GPG encrypt a directory directly?
Ordinary gpg symmetric encryption processes a file, so create a tar archive first. GnuPG also provides gpgtar to archive and encrypt files or directories.
Does GPG remove the original file after encryption?
No. GPG writes a separate encrypted output and leaves the source file in place, so keep it until you have verified a successful restore.
What if I lose the symmetric passphrase?
A symmetric GPG file cannot be decrypted without its passphrase. Use a separately stored original or passphrase backup if you have one.
Should I use Info-ZIP encryption for confidential files?
No. Info-ZIP describes its built-in encryption as weak, so use GPG for confidential files instead.