
A private-key passphrase prompt is for unlocking your local key, not for supplying the remote account password. I’m hooked by the contrast: SSH may use a key already available to your client without asking for a password.
Consider what your computer asks the destination to do when you start a login. The ssh client and sshd server roles will show you which side initiates that encrypted connection and which side accepts the login.
What is SSH in Linux?
Secure Shell (SSH) is a protocol that connects your computer to another through an encrypted session so you can log in as a particular account. The ssh command in Linux starts the client for that connection.
OpenSSH supplies both the ssh client that initiates your connection and the sshd server program that accepts your login on the destination.
| Component | What it does | What you supply |
|---|---|---|
| SSH client | Starts the connection from your computer | A destination and remote username |
| SSH server | Accepts connections and authorizes the account | A listening port and an allowed login method |
| Server host key | Identifies the server to your client | A fingerprint confirmed through a trusted channel |
| User password or key | Authenticates your remote account | Credentials for that account, not your local login |
The OpenSSH client manual separates logging in from executing a remote command. Both use the same encrypted connection, but only an interactive login leaves you at a remote shell prompt.
Prerequisites for an SSH connection
You need a reachable destination with an SSH server and an account you are allowed to use. The default connection port is 22, unless the administrator configured another port.
- An SSH client on the computer where you type the command.
- The destination’s hostname or IP address and its listening port.
- A remote username and either its password or an authorized private key.
- The server’s host-key fingerprint from its administrator or a trusted console.
Check whether the client is available with uppercase -V. It prints the installed version and exits without contacting a server.
ssh -V
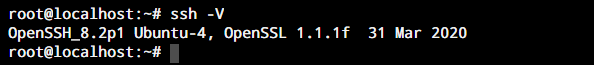
The version screenshot demonstrates a client check, not proof that a remote host accepts connections. The connection example below also runs with OpenSSH 10.5p1 on Ubuntu 24.04, so you do not need the exact build shown in the image.
If ssh is unavailable on Ubuntu or Debian, install the client package. This requires sudo permission on your local computer.
sudo apt install openssh-client
Ubuntu’s OpenSSH documentation names openssh-client for outgoing connections and openssh-server for accepting incoming ones. You do not need to install a local server merely to connect elsewhere.
If you administer the destination, find its IP address there before choosing the connection target. A private address also requires a route from your network, such as an appropriate virtual private network (VPN).
Step 1: Connect to the remote account
Type the remote username before the @ sign and the destination after it. In this example, admin is the remote account and server.example is a placeholder hostname that you must replace.
The username selects an account on the destination, so it need not match the username on your own computer. Leaving it out makes SSH use your local username unless client settings choose another account.
A first connection can display a host-key fingerprint before asking for account credentials. Compare that fingerprint with the value supplied by the administrator or your trusted server console before accepting it.
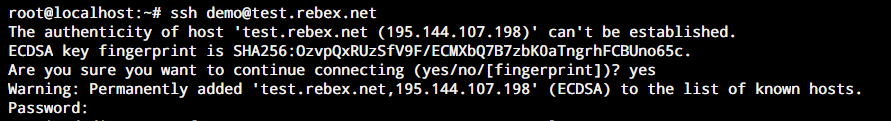
After you accept a matching key, OpenSSH records it in ~/.ssh/known_hosts to detect unexpected changes on subsequent connections.
The fingerprint belongs to the server, while the password prompt belongs to the account you requested. Password input does not display characters as you type, and a password prompt alone does not establish that authentication succeeded.
Enter the remote account’s password if the server allows password authentication. For key-only authentication, you need a private key whose matching public key is authorized for that account.
Step 2: Select the port and private key
Lowercase -p selects the server’s listening port when it differs from 22, without changing the server’s configuration.
ssh -p 2222 [email protected]
The example requests port 2222, so substitute the port your administrator gives you. If you need to change the server itself, follow the separate SSH port-change procedure rather than changing only the client command.
| Option | Use it when | Boundary |
|---|---|---|
| -p 2222 | The server listens on port 2222 | Use lowercase -p with ssh |
| -i ~/.ssh/id_ed25519 | You need to select a private key | Its public key must be authorized for the account |
| -o IdentitiesOnly=yes | Your agent offers other keys before the intended one | Restricts authentication identities to configured keys |
| -l admin | You prefer a separate username option | Alternative to admin@hostname |
| -v | You need connection diagnostics | Debug logs can disclose account and destination details |
| -4 or -6 | You need a particular IP address family | The destination still needs a reachable address |
| -C | You want to compress session data | It is not a general speed guarantee |
| -a | You want agent forwarding disabled | Do not enable -A without understanding the remote trust boundary |
For a server that accepts your Ed25519 key, combine the port and identity options. Replace the key path with your own private key, which stays on your client.
ssh -p 2222 -i ~/.ssh/id_ed25519 -o IdentitiesOnly=yes [email protected]
Use the key-based SSH login guide if you have not authorized the matching public key yet. Its private-key passphrase unlocks your local key, independently of the remote account password.
Step 3: Run a command on the server
Append whoami to return the remote account name without opening an interactive shell.
ssh [email protected] 'whoami'
Single quotes protect the command from local shell expansion before SSH sends it to the server. When the command finishes, the client returns after printing its output in your local terminal.
To leave an interactive login, type exit in the remote shell to close the session and return to your local terminal.
exit
SSH runs commands with the remote account’s permissions, so logging in does not automatically grant administrator access. If your task is moving files, use the scp command for copying or rsync over SSH for synchronization instead of pasting file contents into a shell.
Verify the session reaches the intended account
Confirm the remote account before changing files, because a successful login under the wrong username gives you that account’s home directory and permissions.
I ran whoami through an SSH connection to an isolated loopback test account and received ubuntu. The configuration used 127.0.0.1 on port 22222, with a temporary authorized key and a separately trusted host key.
The -F option reads the connection settings from ssh-demo.conf, where ssh-demo selects the Host entry for the example account.
Host ssh-demo
    HostName 127.0.0.1
    User ubuntu
    Port 22222
    IdentityFile ./ssh-demo-key
    IdentitiesOnly yes
    UserKnownHostsFile ./ssh-demo-known-hosts
    StrictHostKeyChecking yes
The test server already authorized the public key matching ssh-demo-key, and ssh-demo-known-hosts contained its trusted host key. To reproduce this arrangement, supply your own authorized account and key, then substitute the destination and its independently confirmed host key.
ssh -F ./ssh-demo.conf ssh-demo 'whoami'
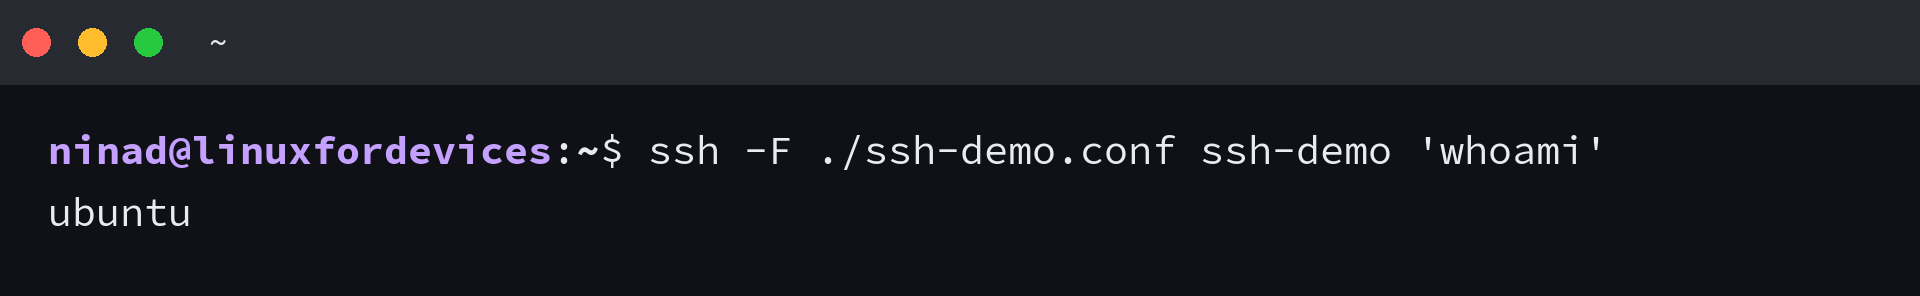
The alias is an example configuration, not an installed hostname or a public service you can connect to. The returned username confirms which account executed the command.
- Match the returned account name to the account you intended to use.
- Confirm the host fingerprint through a trusted channel, not just the hostname shown in a prompt.
- Before a write, confirm the remote path belongs to the intended account.
When SSH connects but login fails
A refused network connection cannot be repaired by choosing another private key. Identify whether SSH reached the server before changing credentials, because transport and account authentication fail at different stages.
| Message or symptom | Stage | What to check |
|---|---|---|
| Connection refused | Transmission Control Protocol (TCP) connection | The destination address, configured port and whether a service listens there |
| Connection timed out | Network reachability | Routing, server availability and firewall rules |
| Could not resolve hostname | Name lookup | The hostname spelling and domain name system (DNS) resolution |
| Permission denied (publickey) | Account authentication | Remote username, selected key and authorized public key |
| REMOTE HOST IDENTIFICATION HAS CHANGED | Server identity | Confirm the new host key through a trusted console before changing known_hosts |
| shell request failed on channel 0 | Session request | Whether the account allows a shell or only a file-transfer subsystem |
Use -v to see whether the connection reaches the host and which authentication method it attempts. Remove identifying details before sharing a debug log.
For a private-key permissions warning, restrict access to the private file using the chmod permission controls. For a timeout, inspect the applicable UFW firewall rules if you administer that server, without opening unrelated ports.
A server can accept a connection but refuse a terminal or shell. The custom-port example in this image reports both requests as failed, so it cannot serve as proof of interactive access.
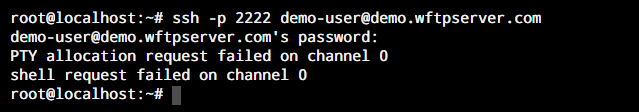
Ask whether the account permits a shell before adding -t, because requesting a terminal cannot override a server policy that denies shell access.
Do not disable host-key checking to clear a changed-key warning. A rebuild can legitimately change the key, but an impersonating server can trigger the same warning, so confirm the identity before replacing the stored entry.
Give the connection a reusable name
Save destination settings under a Host alias when repeating a long command becomes awkward. Put this example in ~/.ssh/config after substituting your server details, and keep specific Host entries before broad defaults.
Host work-server
    HostName server.example
    User admin
    Port 2222
    IdentityFile ~/.ssh/id_ed25519
    IdentitiesOnly yes
The client configuration manual explains why the first obtained setting takes precedence. An alias changes client settings without changing the server.
Uppercase -G prints the effective configuration and exits without authenticating, so inspect its settings before making the next connection.
ssh -G work-server
Once the settings match your intended destination, use ssh work-server to connect. If your next task is reaching a service through that connection, continue with SSH port forwarding rather than exposing the service directly.
SSH connection questions
The server decides which authentication methods and sessions your account may use.
How do I change the username used for an SSH login?
Put the remote account name before the @ sign, or use the -l option. Changing the username in the client does not create that account on the server.
Do I need an SSH server on my computer to connect elsewhere?
You need the SSH client for outgoing connections. The destination needs a server that accepts your account, and Ubuntu packages those roles separately as openssh-client and openssh-server.
Why does SSH not ask for a password?
The server may accept a key already available to your client or may prohibit password authentication. A private-key passphrase prompt unlocks that local key, which is separate from a remote account password.
Does changing the SSH port secure the account?
Selecting another port does not replace account authentication or host-key verification. The server must already listen on that port, and the client must be able to reach it.