
`ip route get 127.0.0.1` reports a local route through `lo`, not just the address assigned to that interface. I like that `ip` can answer a destination question without making an address listing do double duty.
Pin down the network question you need answered. Then choose the `ip` object that fits it.
What the ip command reads and changes
iproute2 provides ip to show or change Linux network state, with objects such as address, link, and route selecting what to inspect or change.
ip [ OPTIONS ] OBJECT { COMMAND | help }
The object is the network state you want to inspect, such as a link or an address. The verb after it can show that state or change it, so read the command from left to right before adding sudo.
Start with the object that matches your question. The ip manual page lists the full grammar and available objects.
| Object | What it shows or changes |
|---|---|
| address or addr | Internet Protocol version 4 (IPv4) and version 6 (IPv6) addresses assigned to network devices |
| link | Interface state and link-layer settings |
| route | Kernel routing-table entries and destination lookups |
| neighbour | Local link-layer neighbour entries |
Find the interface before using a device-specific command
A device name belongs to the system, not to the command you copied. List the interfaces first, then use the exact name from the output.
ip -br link show
The name in the first column identifies the device, and its state follows in the next column. Read both before choosing a device-specific command.
The loopback device is named lo. A virtual private network (VPN) interface has its own system-assigned name, so check this listing instead of copying a name from another machine.
The flags and state describe different things. UP means the interface has been enabled, while LOWER_UP indicates that the lower link is detected, so a mismatch can help distinguish a disabled device from a missing link.
- Read-only inspection commands normally work without sudo.
- Changing an address, route, or link state requires administrative permission.
Inspect an interface and its addresses
Use the address object to see the protocol addresses attached to network devices. The brief form keeps the interface name, state, and addresses together.
ip address show
ip -br addr show dev lo
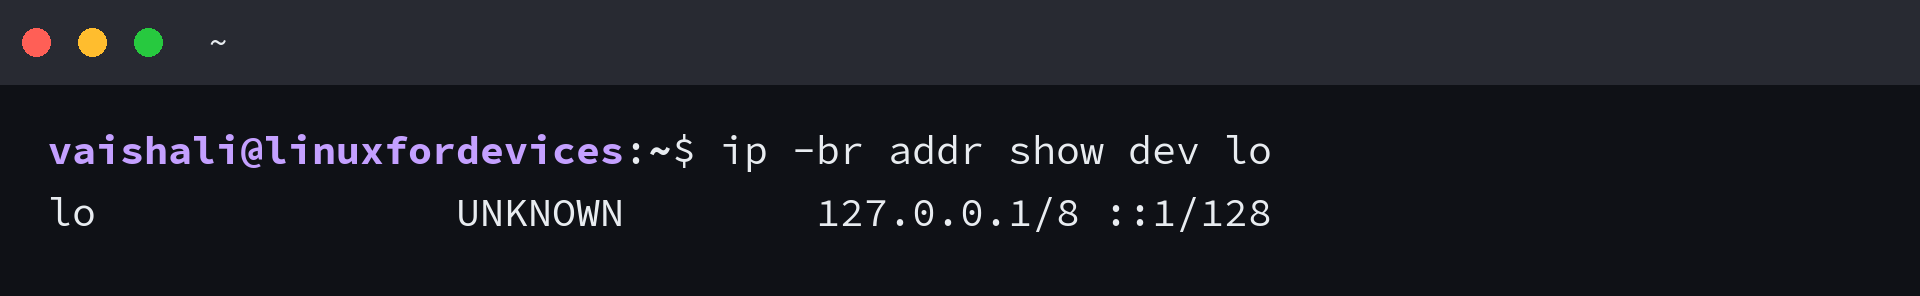
The inet and inet6 lines carry IPv4 and IPv6 addresses, and a suffix such as /24 gives the prefix length. Loopback uses 127.0.0.1 for IPv4 and ::1 for IPv6, keeping that traffic on the host.
The UNKNOWN state on lo is expected because loopback does not report a physical carrier state. An address can also carry scope and lifetime fields that describe where it applies and how long it remains valid.
A device can carry more than one address, including an IPv4 address and an IPv6 address at the same time. The full listing shows those values alongside the interface that owns them.
The capture is limited to loopback, so it shows both address families without exposing a machine’s external interface details. I chose lo because that output is self-contained.
A local interface address and a public address can differ. Our Linux IP address lookup guide explains how a router’s network address translation affects the address an outside service sees.
Filter addresses by family or device
When a machine has several interfaces, add a device filter to narrow the list. Use a family flag when you need IPv4 or IPv6 only.
ip -4 address show dev lo
ip -6 address show dev lo
| Filter | Use it when |
|---|---|
| -4 | You need IPv4 addresses only |
| -6 | You need IPv6 addresses only |
| dev DEVICE | You want one interface instead of the full listing |
| -br | You want a compact address or link summary |
A link-local IPv6 address begins with fe80 and works only on its connected network link. Replace lo with the interface name from the earlier command.
The filter narrows what the command prints, but it does not change the interface or its addresses. Keep the family flag when you are copying an address into a program that accepts only one IP version.
Read the route table and ask which route Linux selects
For one destination, ask Linux which interface and source address it would select with a route lookup. An address listing alone cannot answer that question.
ip route show
ip route get 127.0.0.1
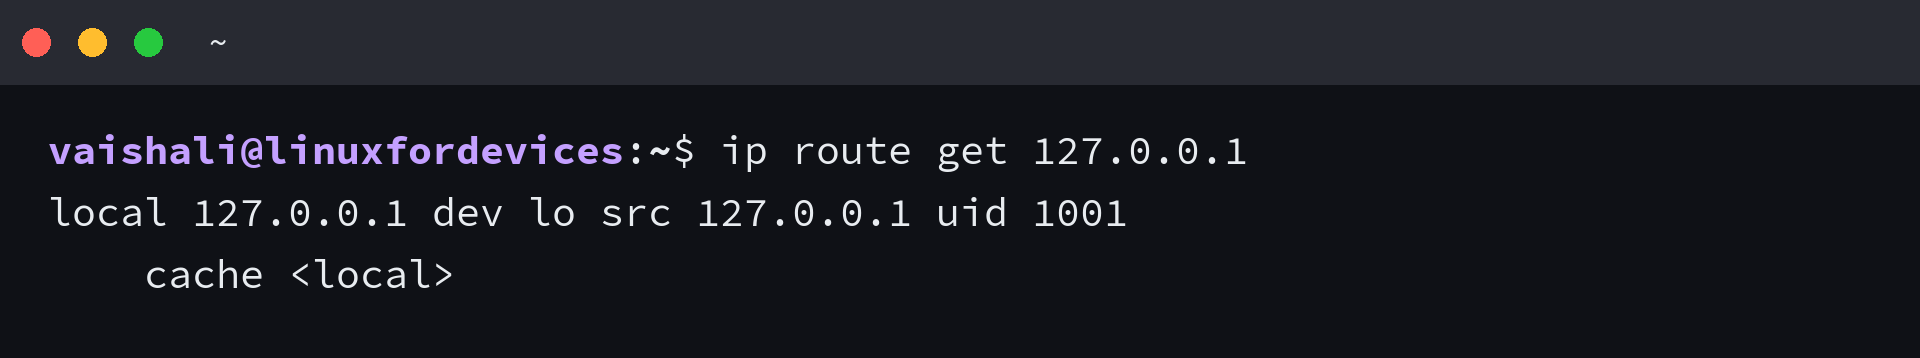
The route output can include via for a gateway, dev for the outgoing interface, and src for the selected source address. The loopback example returns local because 127.0.0.1 never leaves the host.
A default route is the fallback when a destination has no more-specific match in that routing table. Routing rules and additional tables can affect the decision, so a route lookup for the destination is more useful than guessing from the interface list.
A route lookup leaves the table untouched, so I chose it before any route-change example. It reports the kernel’s decision without sending a network probe.
Use the destination you are diagnosing in this lookup, then turn to our Linux traceroute guide when you need to inspect hops beyond your machine.
Add or remove a temporary address
The address object can add or delete a protocol address on a named device. A command needs an unused address and the prefix length that belongs to that network.
Replace both uppercase placeholders before running either form. Do not copy an address from a different subnet or remove a value supplied by a Dynamic Host Configuration Protocol (DHCP) lease unless you know how the connection is managed.
A network manager can renew that lease or reapply the saved settings, which may replace the live change.
sudo ip address add ADDRESS/PREFIX dev INTERFACE
ip -4 address show dev INTERFACE
sudo ip address del ADDRESS/PREFIX dev INTERFACE
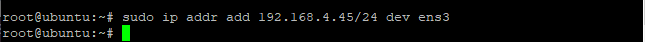
| Operation | Effect | Next check |
|---|---|---|
| add | Attaches the address to the running interface | Show the address list for that device |
| del | Removes the matching address from the interface | Confirm the address no longer appears |
The add and delete forms change live kernel state rather than a saved connection profile. The address must be present on the interface before the delete form can remove it.
The ip-address manual documents both forms. For an Ubuntu address that must survive a reboot, use our static IP guide.
An address change needs administrative permission and can interrupt connectivity if its value or prefix is wrong. Do not apply it to a live interface until you have a recovery path.
Change link state only when you have a recovery path
The link object can enable or disable an interface. Taking down the interface that carries your Secure Shell (SSH) session can disconnect you before you can restore it.
A server without a second console or access path can become unreachable when that link goes down.
Bringing a device up changes its link state, but it does not assign an address or restore a missing route. Check those layers separately after the interface is enabled.
sudo ip link set dev INTERFACE up
sudo ip link set dev INTERFACE down
- Confirm the interface name with ip -br link show.
- Keep a console or a second access path before taking down a remote interface.
- Check the link state and address list after bringing it up.
The link command changes the running interface state, not the network manager’s saved configuration. The ip-link manual describes the available link operations.
Keep persistent settings with the network manager that owns the interface
ip changes the running kernel state. To keep a setting across reboots, use the configuration manager that owns the interface and saves its settings.
Netplan describes interface settings and passes them to a renderer such as NetworkManager or systemd-networkd. Ubuntu uses that layer, while other distributions can use a different configuration owner.
| Task | Use | Boundary |
|---|---|---|
| Inspect a running interface or route | ip address, ip link, or ip route | Read-only query of current kernel state |
| Test a temporary change | ip address add or ip link set | Live state may be replaced by a manager or reset at reboot |
| Keep an address after reboot | Netplan, NetworkManager, or the manager used by your distribution | Use that manager’s configuration and validation steps |
For Ubuntu, our network configuration guide explains how Netplan and its renderer own interface settings. When a name resolves to the wrong address, follow our guide to changing DNS on Linux rather than changing an IP address.
Before changing a route, check the destination-specific decision Linux already makes.
ip route get 1.1.1.1
Frequently asked questions
These details help interpret output that can otherwise look broader than it is.
Can one Linux interface have more than one IP address?
Yes. An interface can carry multiple IPv4 or IPv6 addresses. Use ip address show dev INTERFACE to list the addresses assigned to one device.
Does scope global mean an address is public on the internet?
No. Global scope means the address is not limited to the host or local link. A private address can still have global scope on the interface, and routing or network address translation can keep it off the public internet.